Initially developed by Google, Angular has become one of the leading frameworks for developing web applications. Its popularity is due to the extensive capabilities it offers. However, Angular is complex, and taking full advantage of its features depends on h...
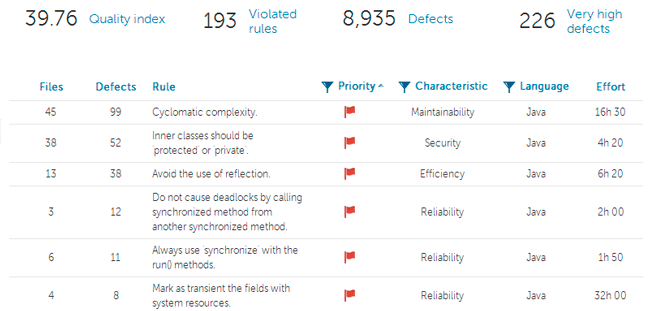
Kiuwan indicators are based on evidence. Part of that evidence —along with intrinsic code metrics— are the defects and vulnerabilities found in the source code analysis Right. What does Kiuwan consider a defect? A defect is a violation to a rule defined in th...
Most of us who have been responsible for the care and feeding of an enterprise application have had to modify someone else’s code. Whether the modification is due to a newly found bug or to enhance existing functionality, changing someone else’s code is an in...
On February 13 we released support for a new programming language: Go (aka Golang). We have added 56 new security rules for Go in our default analysis model (CQM). Visit our Change Log for an explanation on how to view these rul...
High-level programming languages have gone a long way since the invention of Short Code in 1949. New languages are being created all the time, sometimes as a joke, but most times to deal with specific problems that existing ones cannot solve. Althou...
The CWE/SANS Top 25 lists the most dangerous common software errors that can leave your application vulnerable to bad actors. It’s put together by MITRE and the SANS Institute as part of the Common Weakness Enumeration (CWE) project. The list can help you pri...
Today’s app development processes are incomplete without security integration. Security standards provide safeguards for companies to secure their apps and software from cybersecurity threats. NIST, OWASP, WASC, SEI CERT C and J, CWE, and BIZE...
Initially developed by the UK government’s “SafeIT” program and later expanded by the automotive industry, the Motor Industry Software Reliability Association (MISRA) sought to develop a C programming language subset—or “coding standard,” more colloquially—to...
C# OWASP Top 10: How to Discover Vulnerabilities in a C# Web Application In this article, you’ll learn the top 10 security issues in web applications, as defined by the Open Web Application Security Project (OWASP Top 10 – 2017). For each issue, you...
Legacy “business-oriented” languages present unique challenges for software security. Unfortunately, there is a lack of awareness about the security risks of these languages. In this post, we will focus on the security vulnerabilities inherent in busin...
Application security is no longer an afterthought. Developers now prioritize security due to the exponential risk of cybercrime. Developers need to pay more attention to security as it is a crucial aspect of app development. Application security solutions lik...
Software tools for code analysis let developers create code that is less bug-ridden and more secure. They find problems that are hard for human readers to spot and produce unpredictable run-time errors. Along with dynamic tests such as unit testing, they’re a...